
Operating System
Data breaches cost companies billions annually—yet many overlook internal safeguards as their first line of defense. These 10 proven strategies empower cybersecurity leaders to fortify data protection from within, reducing vulnerabilities before threats materialize.
Employee Cybersecurity Training Programs
Your employees might be your biggest security risk—or your strongest line of defense. Since human error causes 90% of breaches, role-specific cybersecurity training transforms teams from accidental targets into vigilant defenders against phishing and social engineering.
Programs like KnowBe4’s Security Awareness Training or SANS Security Awareness offer interactive simulations (e.g., fake phishing emails) to teach real-world recognition skills. Customizable modules cover everything from password hygiene to recognizing CEO fraud schemes, with progress tracking to ensure compliance. Many platforms integrate with HR systems for automated reminders and role-based assignments, like extra finance training for payroll staff.
Ideal for companies of all sizes, these programs are especially critical for SMBs with limited IT budgets—where one click on a malicious link can cripple operations. Start with a quarterly training refresh to keep defenses sharp. 💡
Multi-Factor Authentication Enforcement
Passwords alone are like leaving your front door unlocked—99.9% of credential theft exploits weak or reused passwords. Multi-Factor Authentication (MFA) enforcement adds an extra layer by requiring biometric scans (fingerprint/face ID), hardware tokens, or time-based codes beyond just a password, making unauthorized access nearly impossible.
Modern MFA solutions like Microsoft Authenticator, Duo Security, or YubiKey integrate seamlessly with Active Directory, cloud apps, and VPNs, enforcing verification for every login without disrupting workflows. The biometric + token combo thwarts phishing and brute-force attacks, while session monitoring flags suspicious activity in real time. Even if a password is stolen, the attacker still needs physical access to your device or a second factor.
This safeguard is non-negotiable for finance, healthcare, and legal firms, but even startups handling customer data should adopt it. With zero trust architectures becoming standard, MFA isn’t optional—it’s the baseline for modern security. ⚡
Data Classification and Labeling Policies
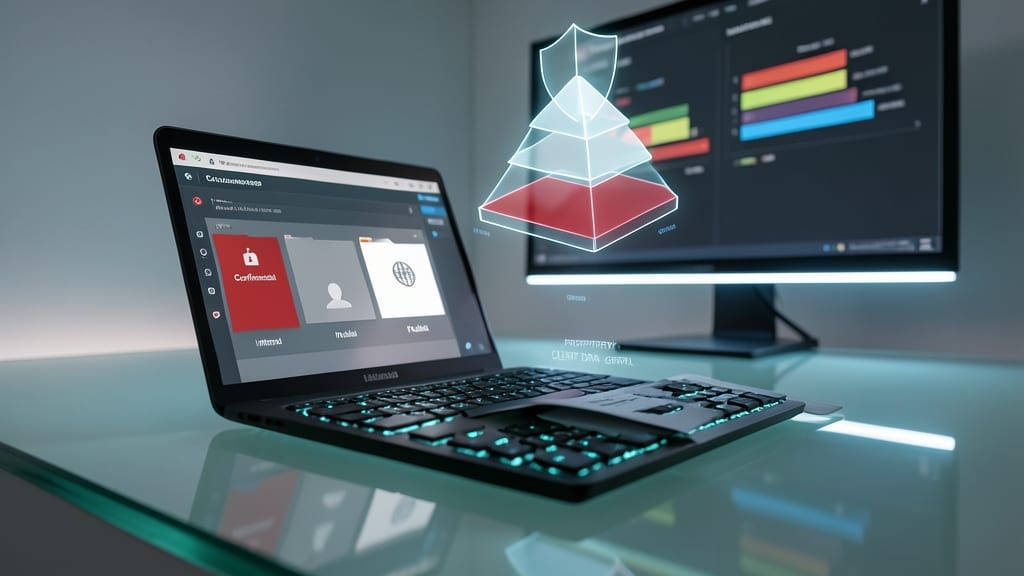
Not all data deserves the same level of protection—and neither should the time spent securing it. Data classification and labeling policies automatically tag files with sensitivity levels (e.g., Confidential, Internal, Public), ensuring your most valuable intellectual property gets the highest priority without manual oversight.
With tools like Microsoft Purview or Symantec Data Loss Prevention, you can enforce role-based access controls that adapt to labels, while automated workflows block unauthorized sharing of sensitive files. The best systems integrate with cloud storage (SharePoint, OneDrive) and email gateways to scan content in real time, reducing human error in enforcement.
Ideal for companies handling trade secrets, client data, or R&D files, these policies turn security from a checkbox into a self-sustaining shield. 💻
Endpoint Detection and Response Systems
When malware slips past firewalls or phishing emails bypass filters, Endpoint Detection and Response (EDR) systems act as your last line of defense. Unlike traditional antivirus, EDR continuously analyzes device behavior—spotting suspicious activity like unauthorized software installs or lateral movement by attackers in real time.
Top solutions like CrowdStrike Falcon or SentinelOne combine AI-driven threat detection with automated response capabilities. They monitor endpoints for anomalies such as unusual process executions, unexpected network connections, or cryptomining activity, then isolate compromised devices before threats escalate. Integration with SIEM tools ensures alerts trigger immediate investigation.
Ideal for mid-sized to large enterprises with distributed networks, EDR transforms reactive security into proactive defense. 💻
Privileged Access Management Controls
Think of your IT environment as a high-security vault—without strict access controls, even well-meaning employees could accidentally (or intentionally) compromise critical systems. Privileged Access Management (PAM) solves this by enforcing the principle of least privilege, ensuring only verified personnel can modify servers, databases, or sensitive configurations.
Modern PAM solutions like CyberArk or BeyondTrust automate session monitoring, credential rotation, and activity logging for admin accounts. They can even revoke access instantly if suspicious behavior is detected, while granular audit trails provide forensic evidence during investigations. For example, a financial services firm reduced insider threats by 70% after implementing just-in-time access for developers.
This isn’t just for enterprises—small teams managing cloud infrastructure (e.g., AWS, Azure) benefit from PAM’s automated workflows to prevent credential abuse. Start with a free trial of tools like Thycotic to test how least-privilege access transforms your security posture. 🌟
Encrypted Communication Channels
Imagine sending a confidential contract or brainstorming sensitive product details—only for it to be intercepted mid-transit. End-to-end encrypted communication channels ensure your messages, files, and chats stay locked down, even if intercepted. Unlike standard email, these tools encrypt data at the sender’s device and only decrypt it at the recipient’s, making them ideal for legal, finance, or R&D teams.
Platforms like ProtonMail (for email) or Signal (for messaging) offer military-grade encryption with zero-access policies, meaning not even the provider can read your content. For file transfers, VeraCrypt or Tresorit add an extra layer of protection by encrypting files before upload. These tools integrate seamlessly with existing workflows, replacing unsecured Slack channels or email with audit logs to track access and activity.
Perfect for industries handling patient records, trade secrets, or client data, encrypted channels turn every conversation into a secure vault. Whether you're a startup or enterprise, the peace of mind is worth the minimal setup. ✨
Regular Security Audits and Penetration Testing
Think of security audits and penetration testing as your company’s fire drill for cyber threats—except instead of practicing evacuations, you’re exposing weaknesses before hackers exploit them.
Automated tools like Burp Suite or Nessus scan for misconfigurations, while ethical hackers simulate attacks on firewalls, APIs, and applications to find gaps. These tests often reveal issues even advanced systems miss—like outdated software or weak authentication protocols—before they become costly breaches.
Ideal for companies handling sensitive data (healthcare, finance, or proprietary tech), these audits should run quarterly or after major system updates. The peace of mind? Knowing your defenses can withstand real-world threats. 💻
Secure Remote Work Policies
Remote work isn’t just convenient—it’s a security minefield if not properly managed. Without the right policies, off-site employees become the weakest link, exposing company data to risks like unsecured Wi-Fi or lost devices. The solution? A comprehensive remote work security framework that bridges the gap between office and home environments.
Start with mandatory VPN usage for all remote connections, ensuring traffic is encrypted even on public networks. Pair this with full-disk encryption (like BitLocker or FileVault) on company-issued devices, so stolen laptops become digital fortresses. Add real-time activity monitoring—tools like CrowdStrike or Microsoft Defender for Endpoint track suspicious behavior without invading privacy, flagging anomalies like unusual login times or data exfiltration attempts.
This approach is perfect for companies with hybrid teams or fully remote workforces. It keeps sensitive data safe while maintaining productivity, proving security doesn’t have to be a productivity killer. ✨
Automated Data Loss Prevention Tools
Even the most careful employee can accidentally leak sensitive data—whether by plugging in an unapproved USB drive or uploading files to the wrong cloud folder. Automated Data Loss Prevention (DLP) tools act as an invisible shield, scanning and blocking unauthorized transfers in real time without slowing down workflows.
Solutions like Forcepoint DLP or Symantec DLP monitor email attachments, cloud uploads, and removable storage with AI-driven policies. They can even detect PII (Personally Identifiable Information) or trade secrets in documents and trigger alerts before data leaves your network. Integration with Microsoft 365 or Google Workspace makes them seamless for modern teams.
Ideal for industries handling healthcare records, financial data, or proprietary research, these tools reduce compliance risks while giving IT teams visibility into potential threats. The peace of mind? Priceless. ✨
Incident Response and Recovery Plans
When a breach happens, every minute counts—and a predefined incident response plan turns chaos into control. Unlike reactive scrambling, these plans outline step-by-step containment, communication, and recovery protocols to limit damage before it spirals. Think of it as your cybersecurity "fire drill," ensuring your team acts swiftly and consistently under pressure.
Start with clear roles and escalation paths (e.g., IT leads, legal, PR) to avoid confusion during crises. Include real-time monitoring tools (like SIEM systems) to detect breaches faster, and pre-approved templates for stakeholder notifications—customers, regulators, and partners deserve transparency without delays. Document restoration checklists for critical systems, backed by offsite backups and disaster recovery plans to ensure minimal downtime.
This isn’t just for enterprises—small businesses benefit too by using NIST’s free incident response templates or ISO 27035 frameworks. The goal? Reduce downtime by 60% and protect your reputation by showing you’re prepared. 💪